Overview
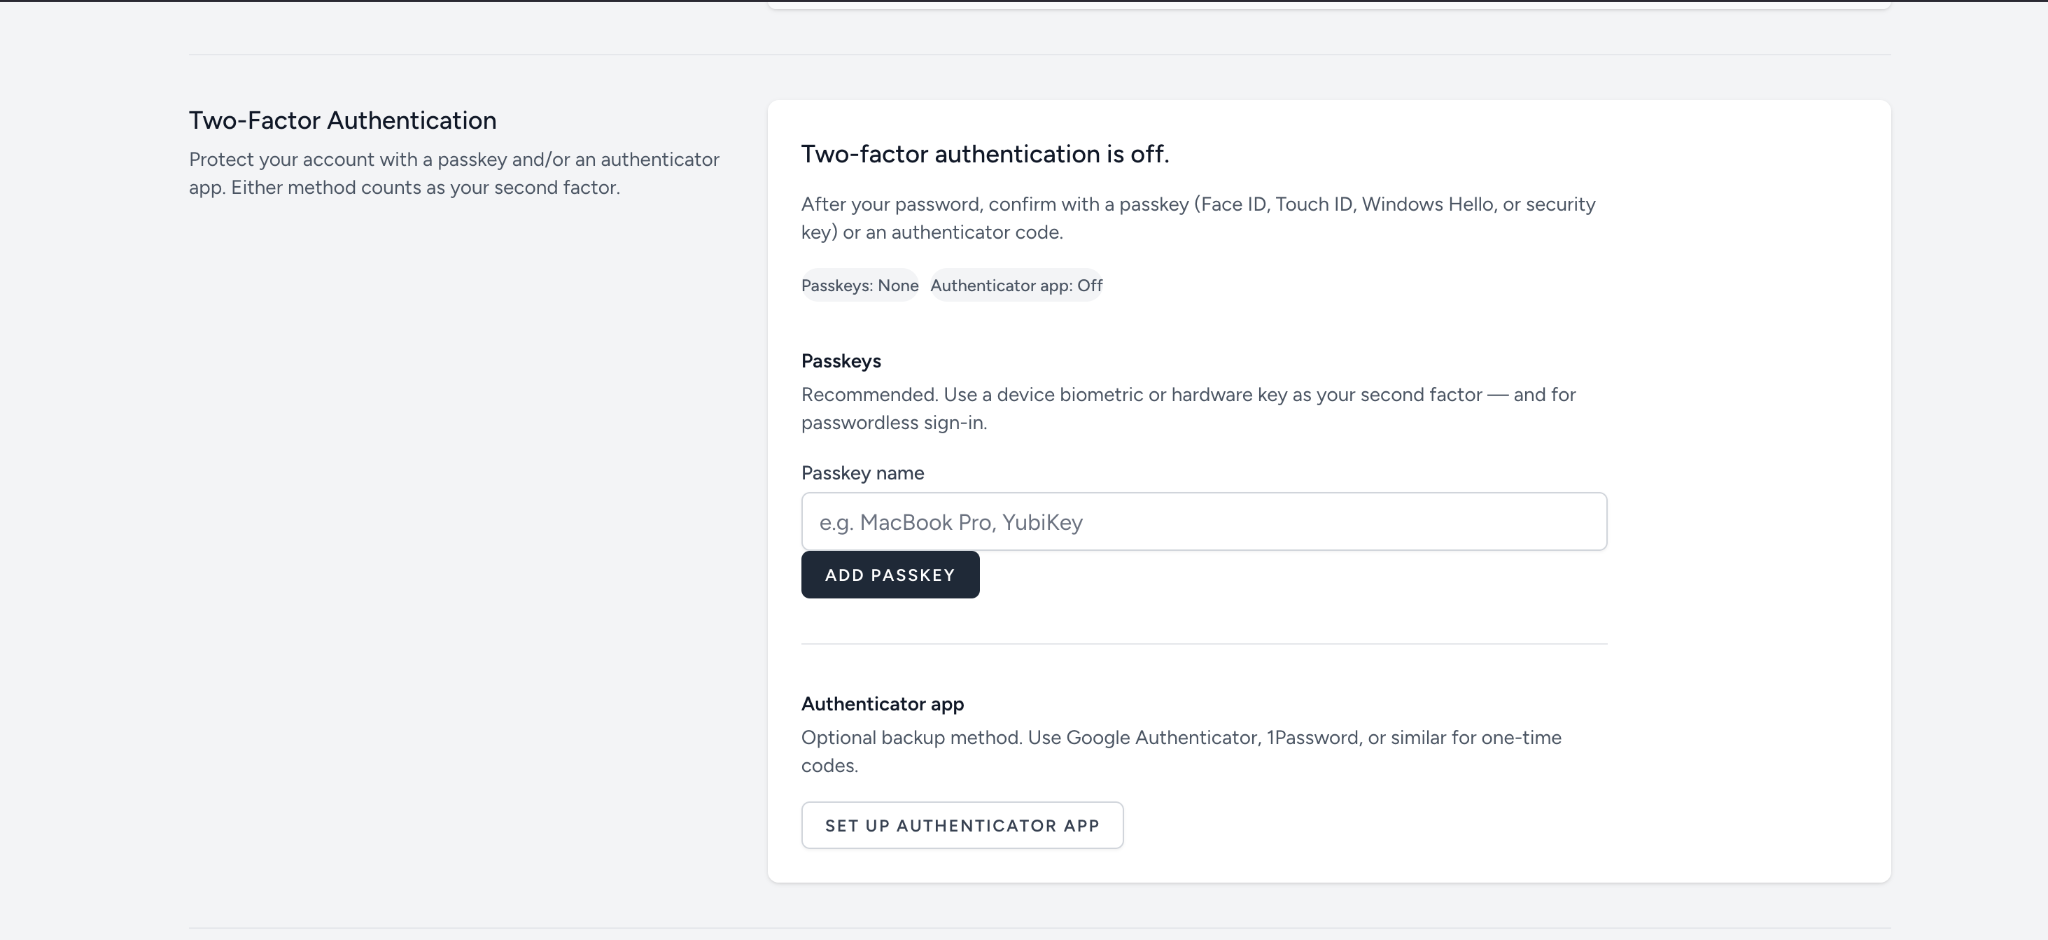
Use the security controls in Profile & 2FA to protect sign-in, review sessions, and add a stronger second factor.
This article is written as a practical reference for account security. Follow the steps in order the first time, then use the headings and screenshots as landmarks when you return later. The screenshots reflect the current Open Accessible Cloud layout shown in September 2026, so labels may move slightly as the dashboard evolves.
Where to look in the dashboard
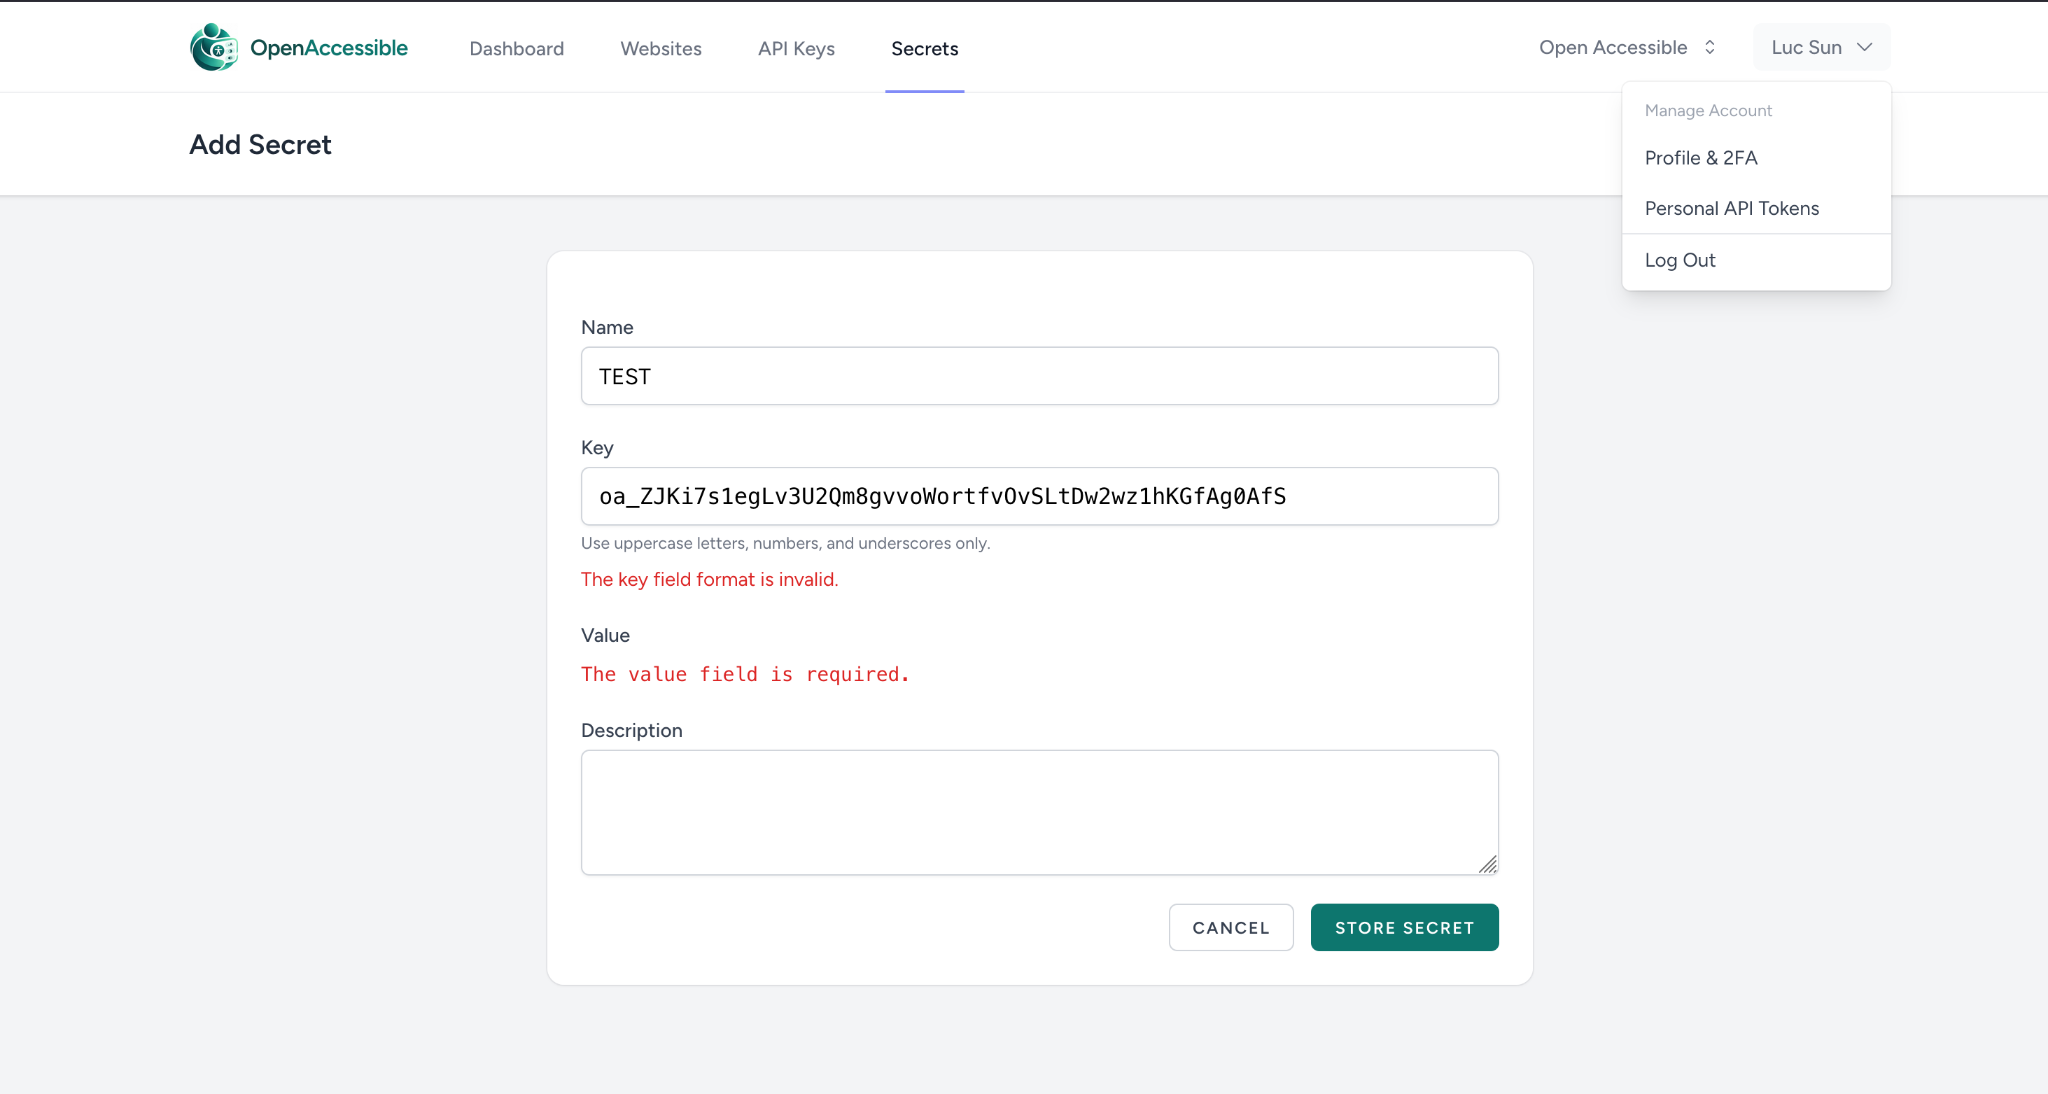
Use the interface landmarks below to get to the right place before making changes. The screenshots are included as guidance so you can match the documentation to what you see in the dashboard.
Before you begin
Confirm that you are signed in to the correct account and, when applicable, that the organization selector in the upper-right corner shows the organization you intend to manage. If you work with multiple websites, verify the domain before changing settings.
For changes that can affect a live site, take note of the current configuration first. A screenshot, copied setting value, or short change note makes rollback much easier. Avoid changing unrelated options at the same time; smaller changes are easier to verify and troubleshoot.
Understanding the account and organization menus
The dashboard separates personal account settings from organization settings. Your name in the upper-right corner opens personal controls such as Profile & 2FA and Personal API Tokens. The organization name opens organization-level controls, including Organization Settings and creating another organization.
This distinction is important when troubleshooting permissions. A change to your personal profile does not automatically change organization membership, and organization membership does not replace your personal password, passkey, or authenticator configuration.
Step-by-step workflow
- Identify whether the task is personal or organizational. Personal controls are under your user name; organization controls are under the organization name.
- Open the exact settings area shown in the screenshots. Read the surrounding labels before saving so you do not confuse similarly named account and organization options.
- Make the smallest necessary change. For security settings, add the new factor or credential before removing an older working method whenever the interface allows it.
- Verify the result. Refresh the page and, for sign-in changes, test a new session before considering the change finished.
- Record important ownership changes. If you add or remove team members, note who owns the organization and who can administer it.
Important details
For stronger sign-in protection, a passkey is a good primary second factor when your devices support it. The interface describes passkeys as working with technologies such as Face ID, Touch ID, Windows Hello, or a security key. An authenticator app can be configured as another method for one-time codes.
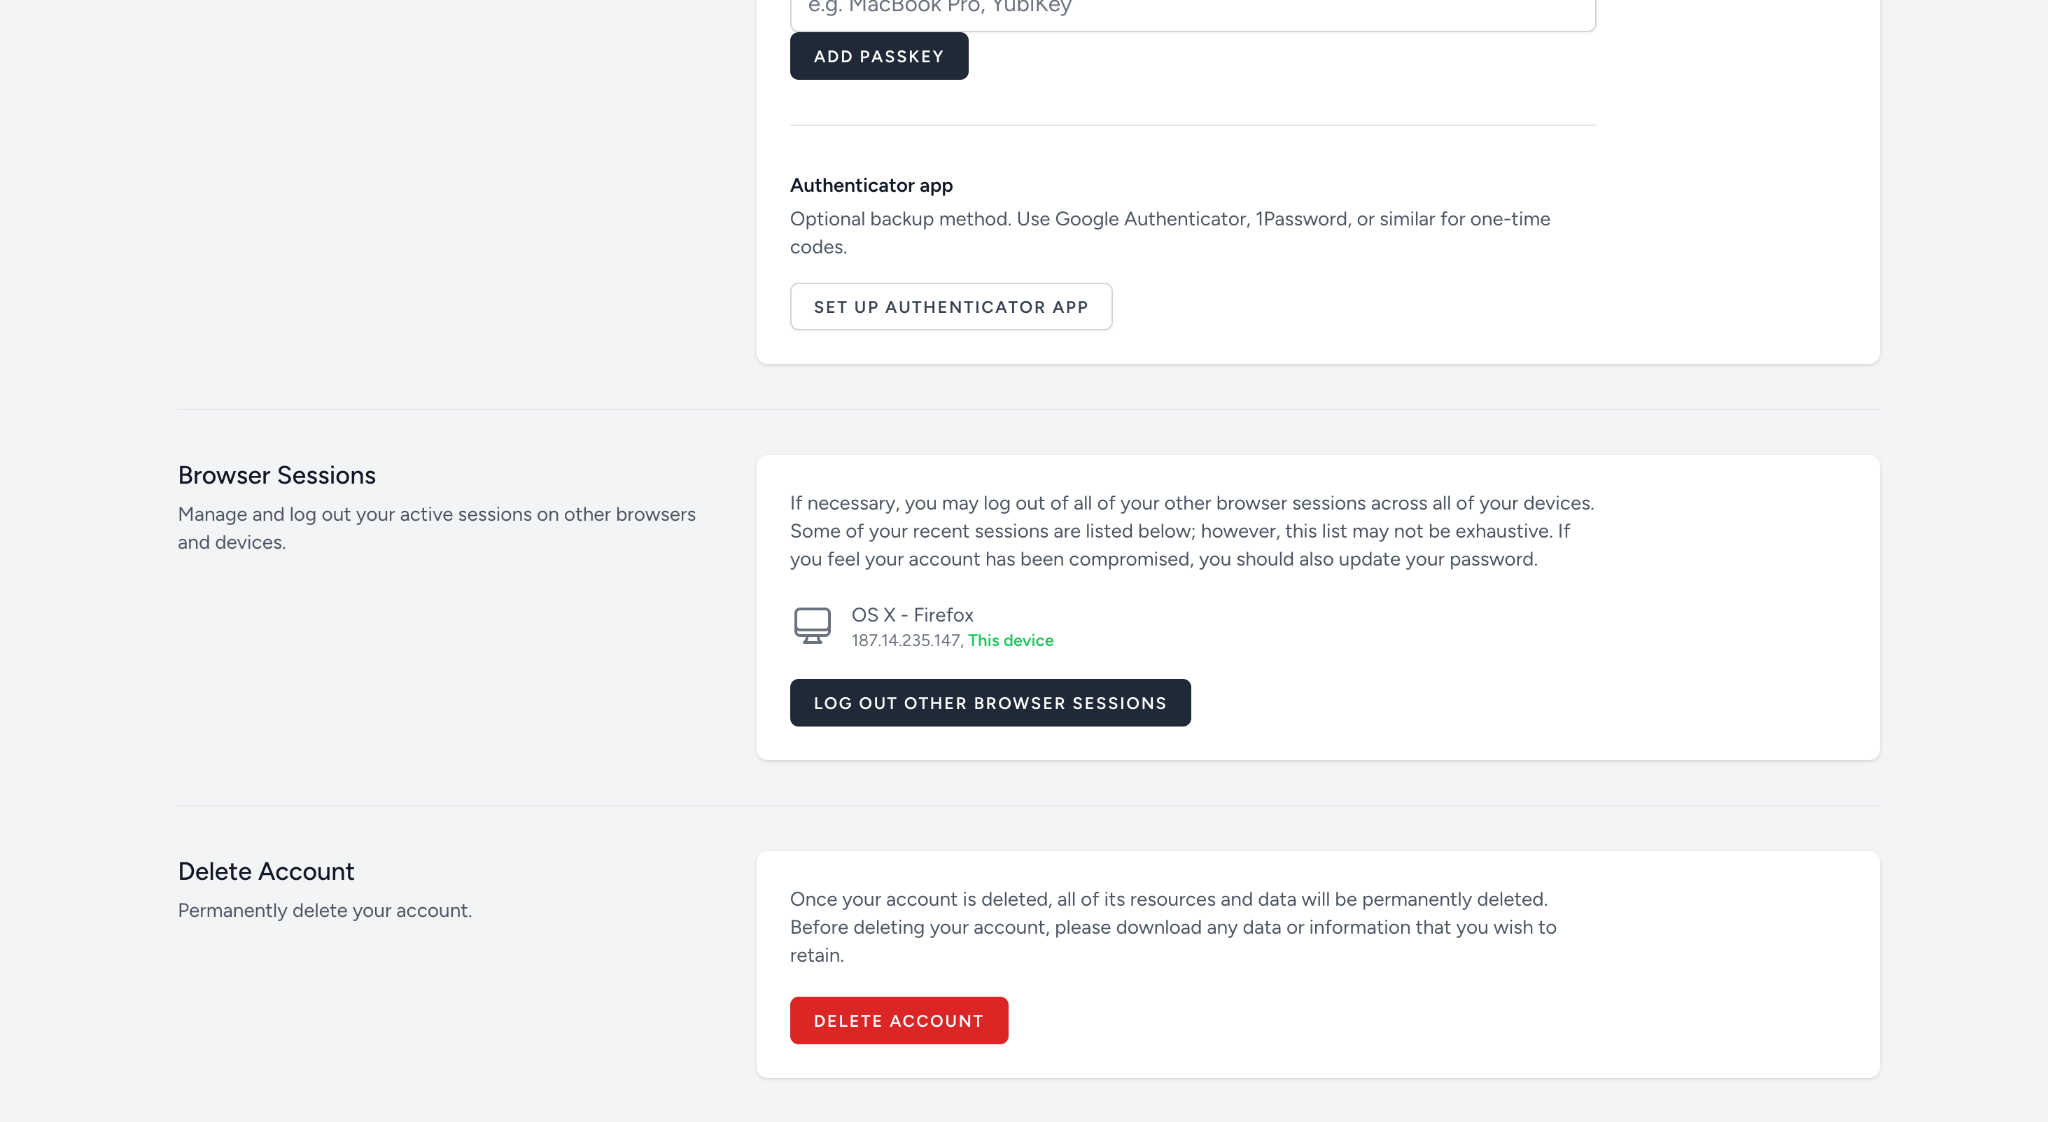
After enabling a new factor, sign out of a secondary browser or open a private window and confirm that you can complete the full sign-in flow. Do this before removing any older recovery path. Then review Browser Sessions and sign out other sessions if you do not recognize them or if a device is no longer under your control.
How to verify the result
Do not stop at the saved confirmation. Reload the relevant page and confirm the visible state matches what you intended. If the change affects authentication, open a fresh browser session. If it affects a website, test the public page as a visitor rather than only the dashboard.
For user-facing changes, check with keyboard input, browser zoom, and a narrow mobile viewport. Watch for overlapping fixed controls, clipped dialogs, focus that disappears off-screen, or settings that reset unexpectedly after navigation.
Troubleshooting
If the dashboard does not match these screenshots, first confirm you are in the correct organization and account. UI labels can also change over time, so look for the same concepts—Websites, API Keys, Secrets, organization settings, or Profile & 2FA—even if the exact placement has moved.
For website problems, check the browser developer console and network panel. Look for blocked scripts, 404 responses, Content Security Policy errors, or requests being stopped by a consent manager or extension. For account problems, try a private window and verify that the email address and organization membership are correct before resetting credentials.
Recommended practices
Use descriptive names for websites, keys, tokens, secrets, and team roles. Clear names reduce the chance of editing the wrong resource and make audits easier months later. Avoid putting sensitive values into screenshots, tickets, documentation, or public source repositories.
Review access periodically. Remove old sessions, unused credentials, and team members who no longer need access. For production integrations, document where each credential is used and who is responsible for rotating it.
Next steps
After completing account security, return to the documentation home page and use search to find the next related workflow. Search accepts normal phrases, so queries such as “website branding,” “2FA,” “API token,” or “installation” will surface related guides.
If you are troubleshooting, keep the page URL, browser name, approximate time, and a concise set of reproduction steps. Those details make it much easier to distinguish an account configuration issue from a website integration issue.